

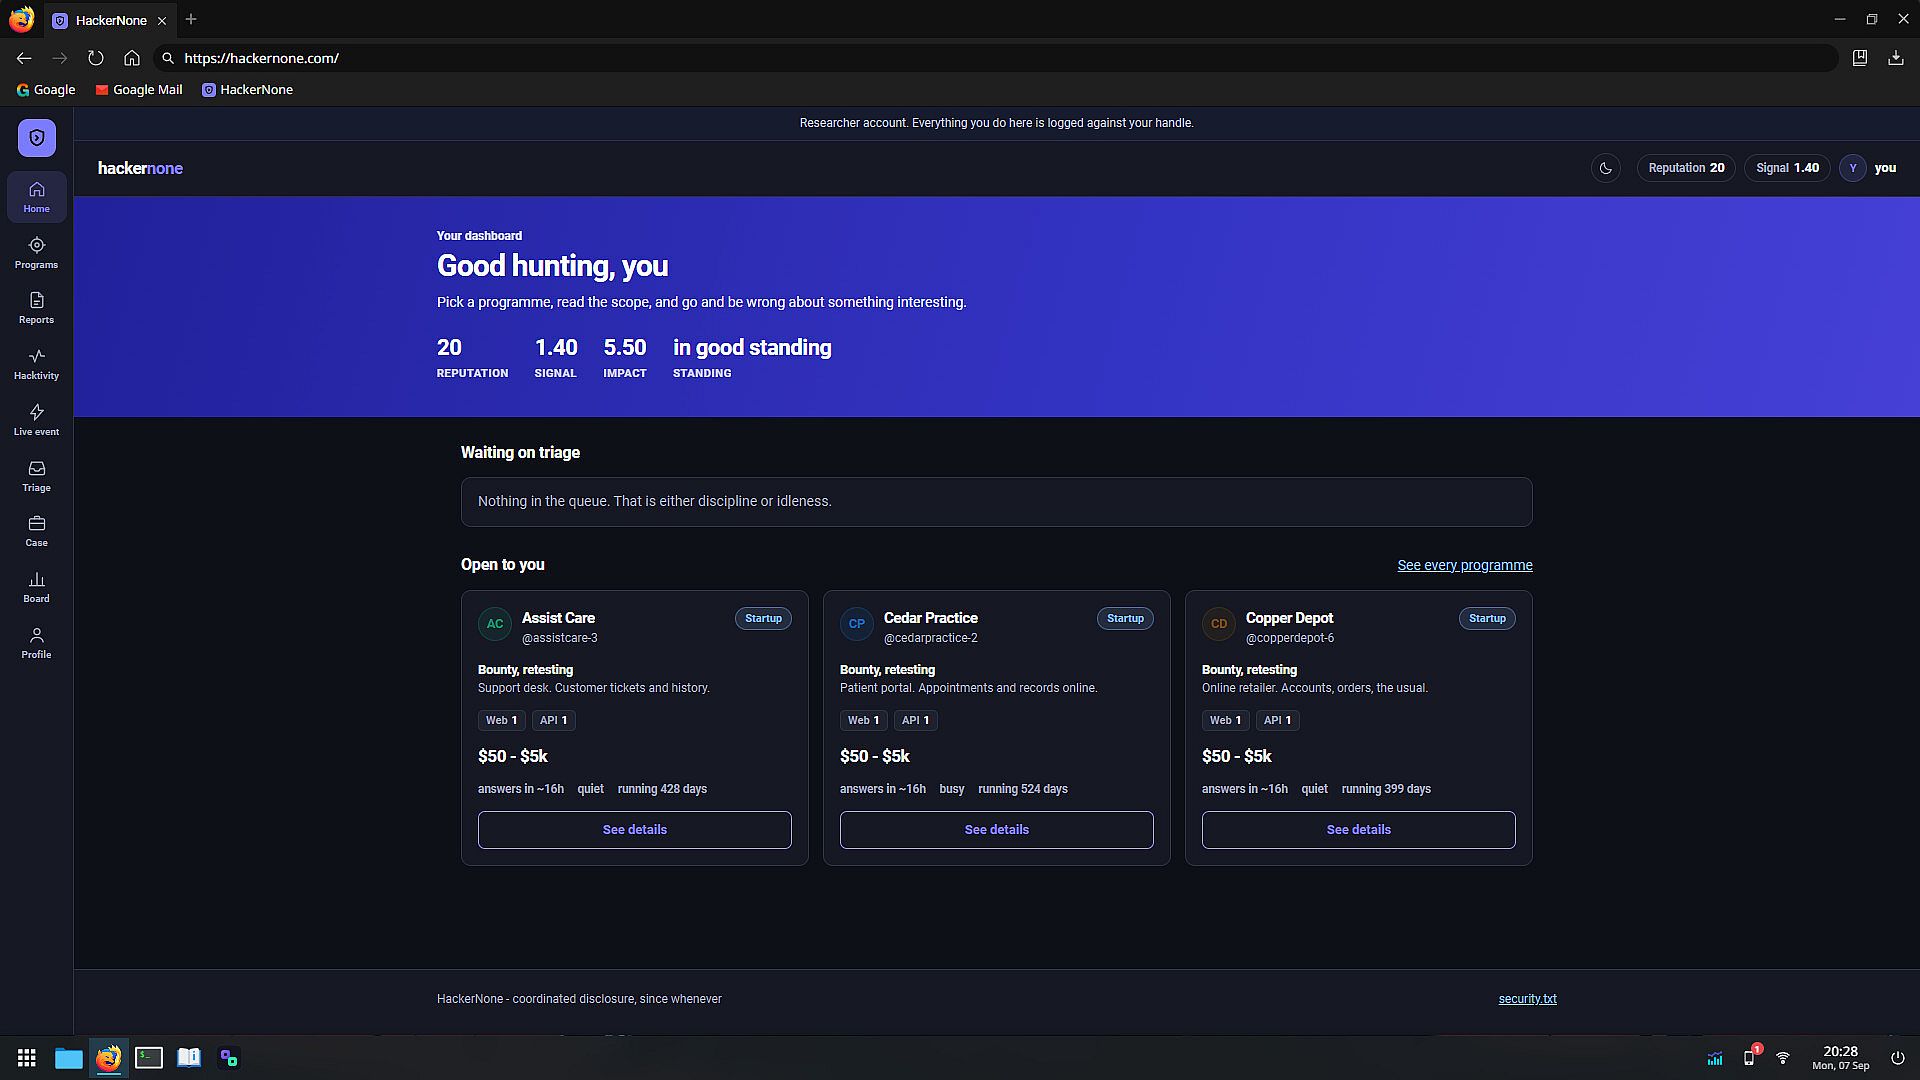
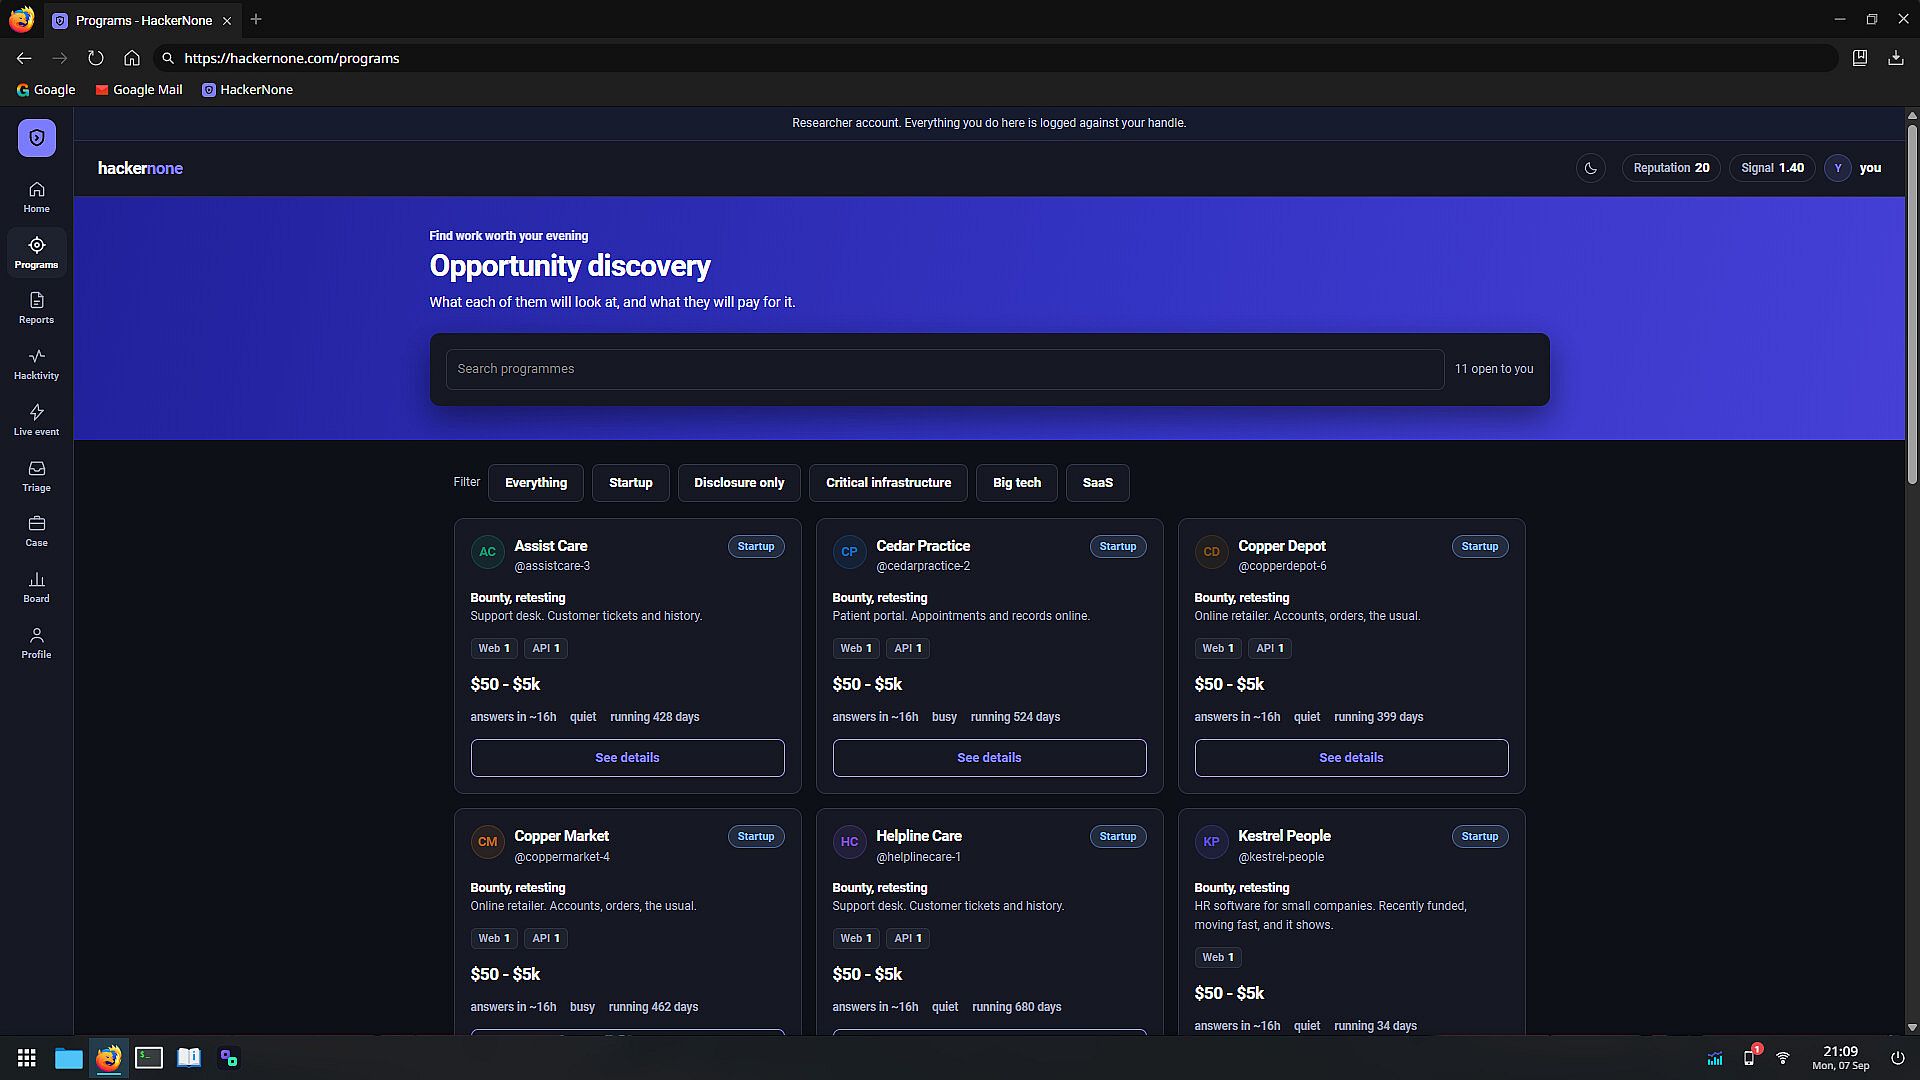
Nobody tells you where the bugs are. A programme page gives you a scope list, a policy, a payout table and how picked-over the target already is. Everything else is browsing the site, reading its JavaScript, running recon in the terminal, and noticing the one thing that does not add up.
Finding it
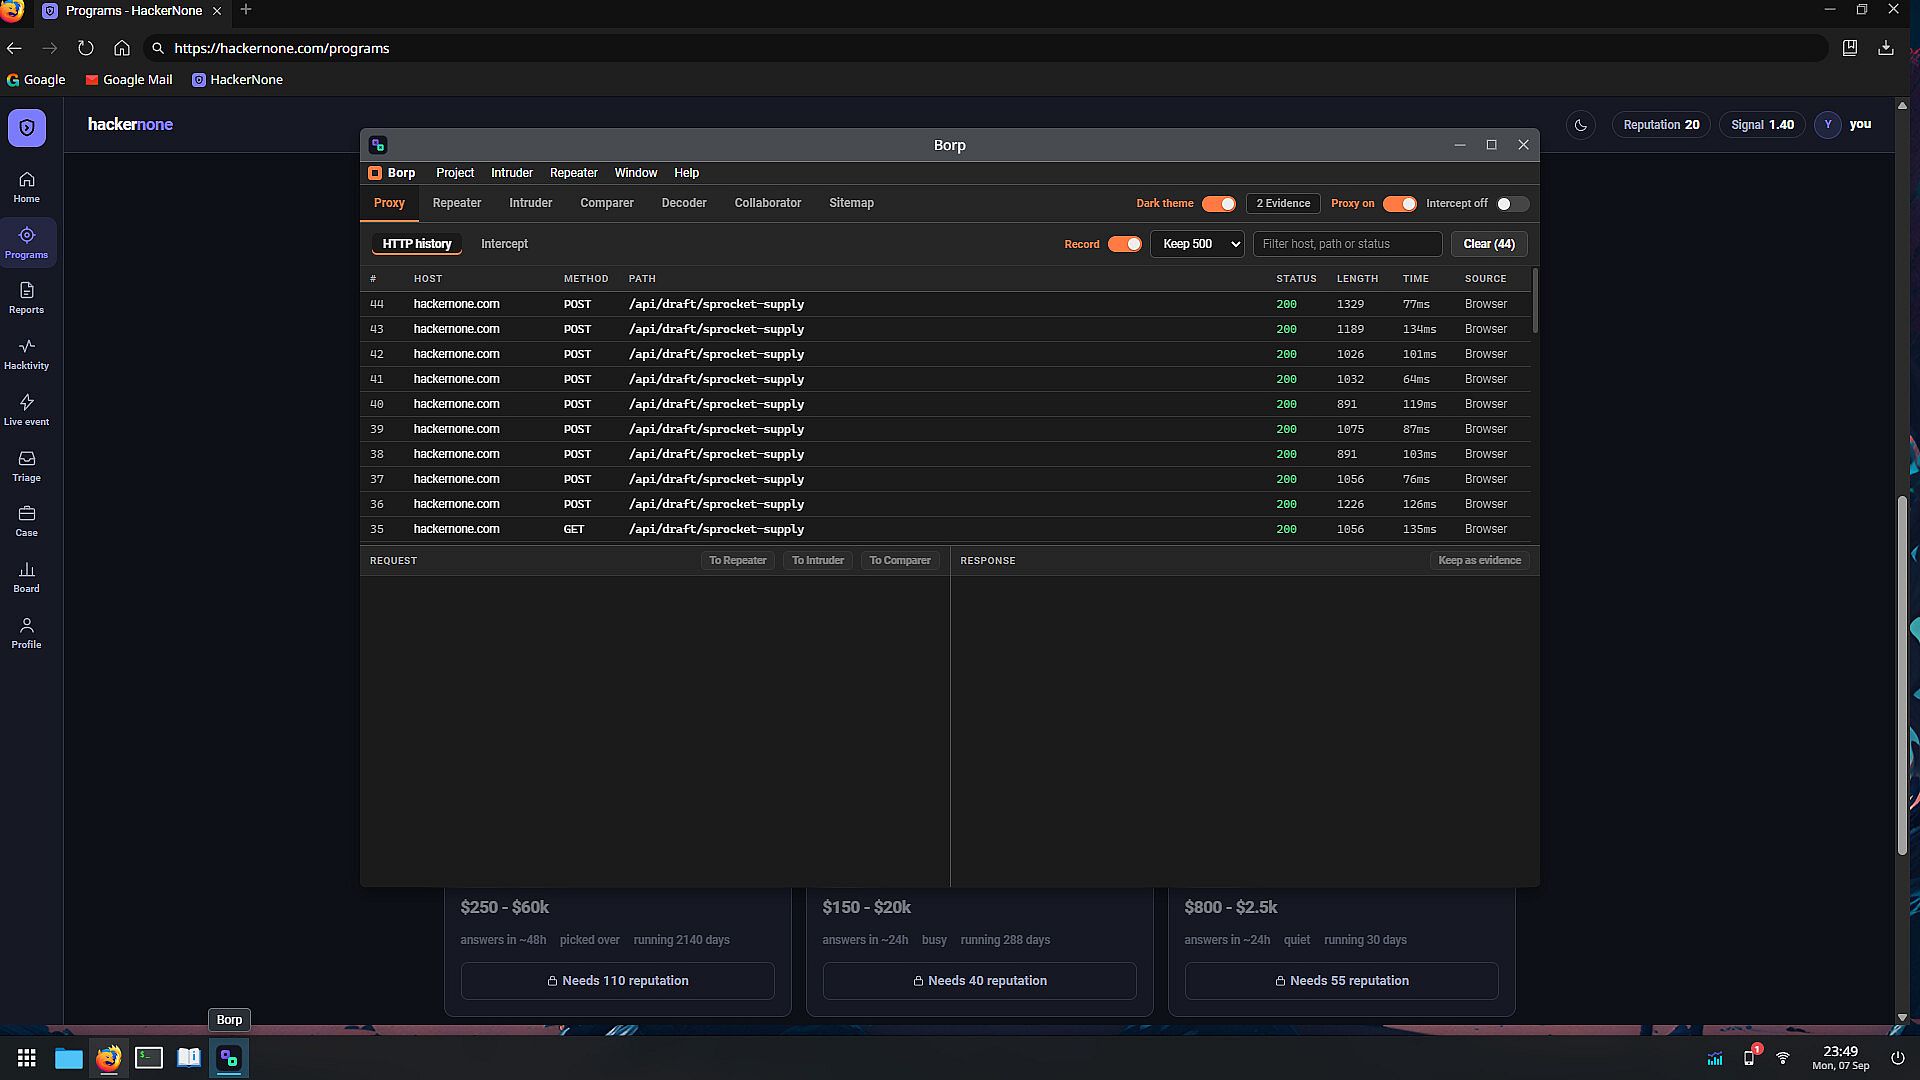
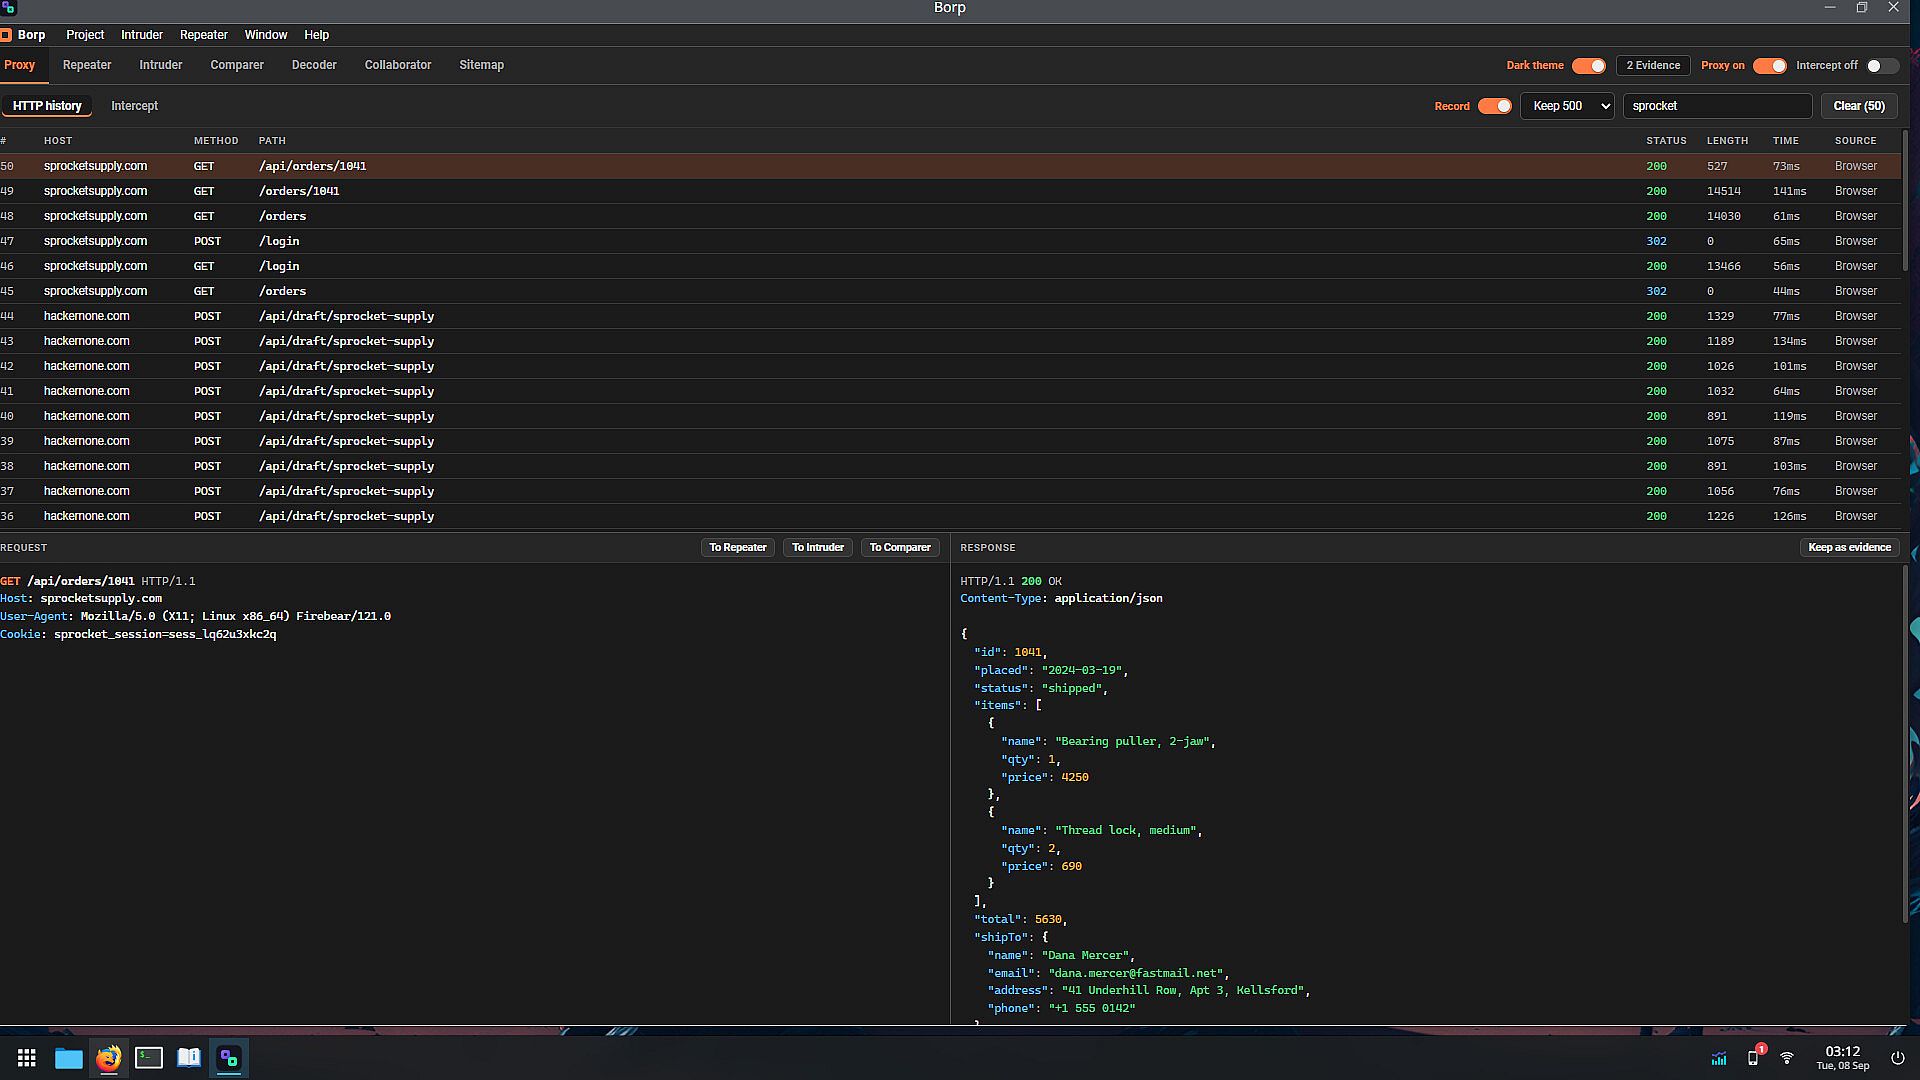
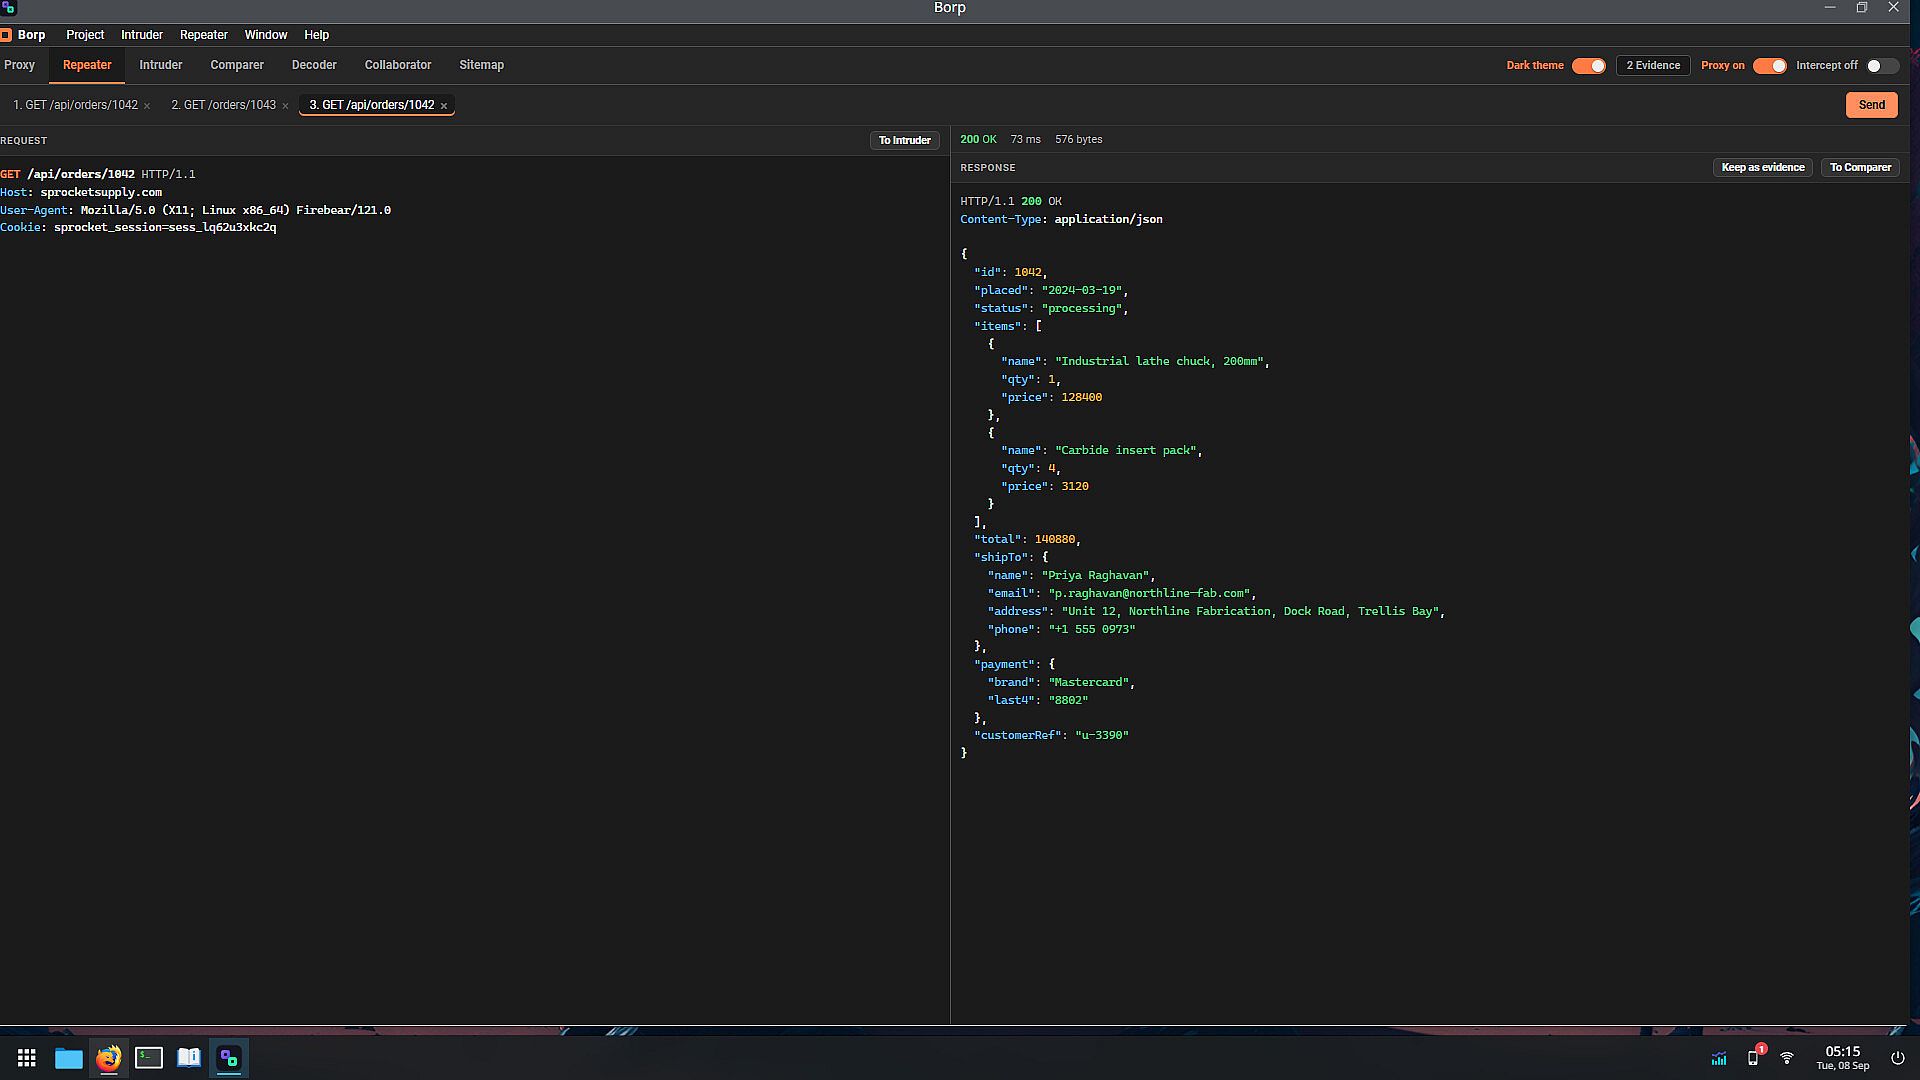
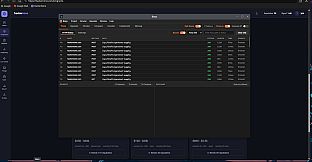
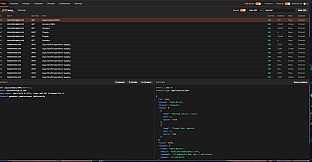
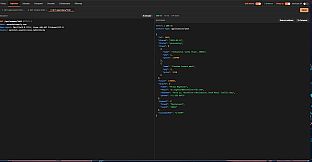
The pack installs Borp, an intercepting proxy, as a desktop app. Proxy the browser through it and every request lands in the history. Hold one in flight and rewrite it before the server sees it, or send it back by hand through Repeater as many times as you want, with whatever headers you want. Findings that produce nothing visible are proved with the collaborator: your payload calls out to a domain that logs the hit, and that log line is the evidence.Twenty-four weakness classes are implemented, all of them real ones: IDOR, broken access control, JWT signature bypass, SSRF, path traversal, stored and blind XSS, SSTI, host header injection, subdomain takeover, secrets committed to source, business logic, race conditions. Each target's flaw genuinely exists in its simulated server. There is no scripted flag to walk into.
Reporting it
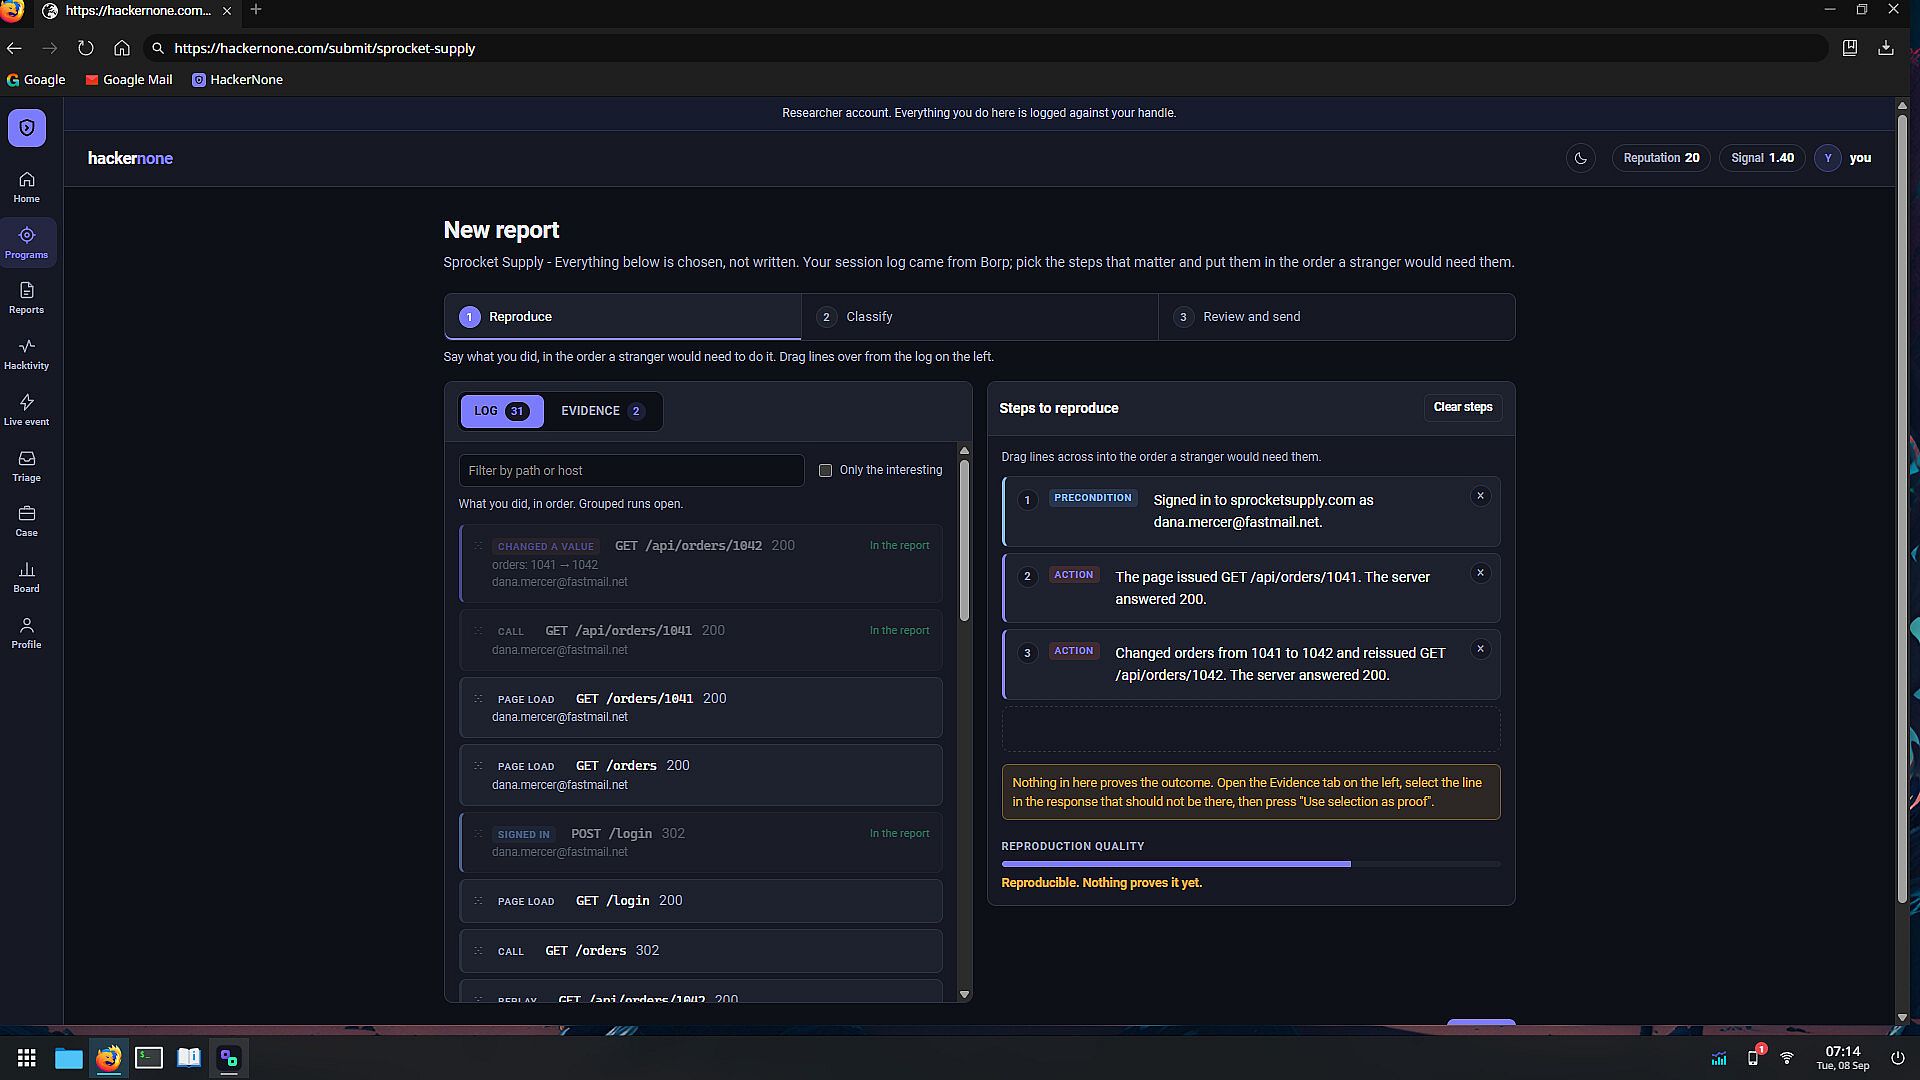
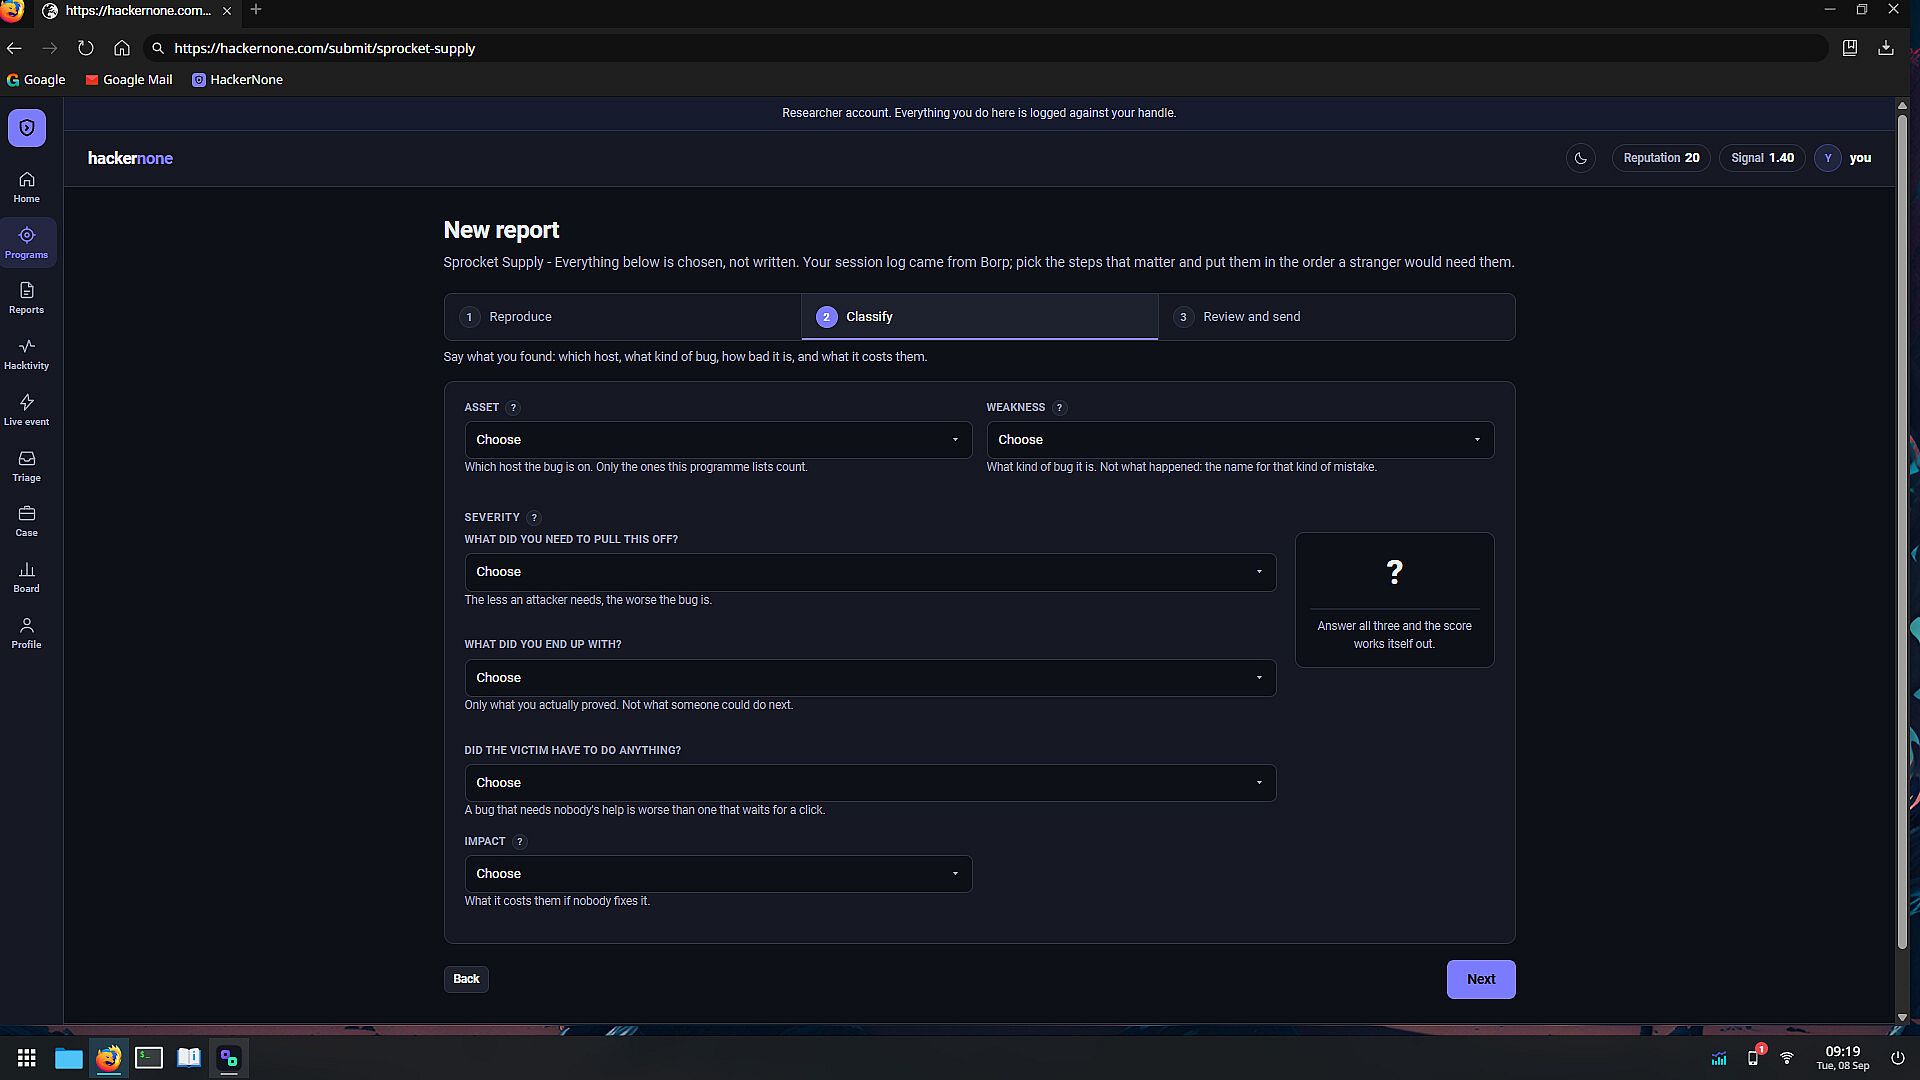
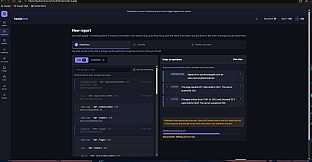
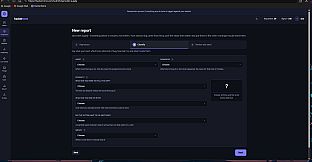
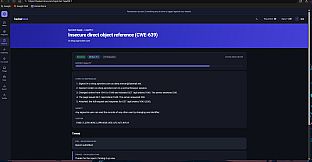
Finding the bug is half the job, and the report is not a text box.Borp records what you did. To write the reproduction you drag the relevant steps out of that log, put them in order, and mark which ones are evidence. Then you classify the finding: which asset, which weakness, and a set of plain-language questions that build the CVSS vector for you. Impact in your own words. A fix, if you have one worth suggesting.
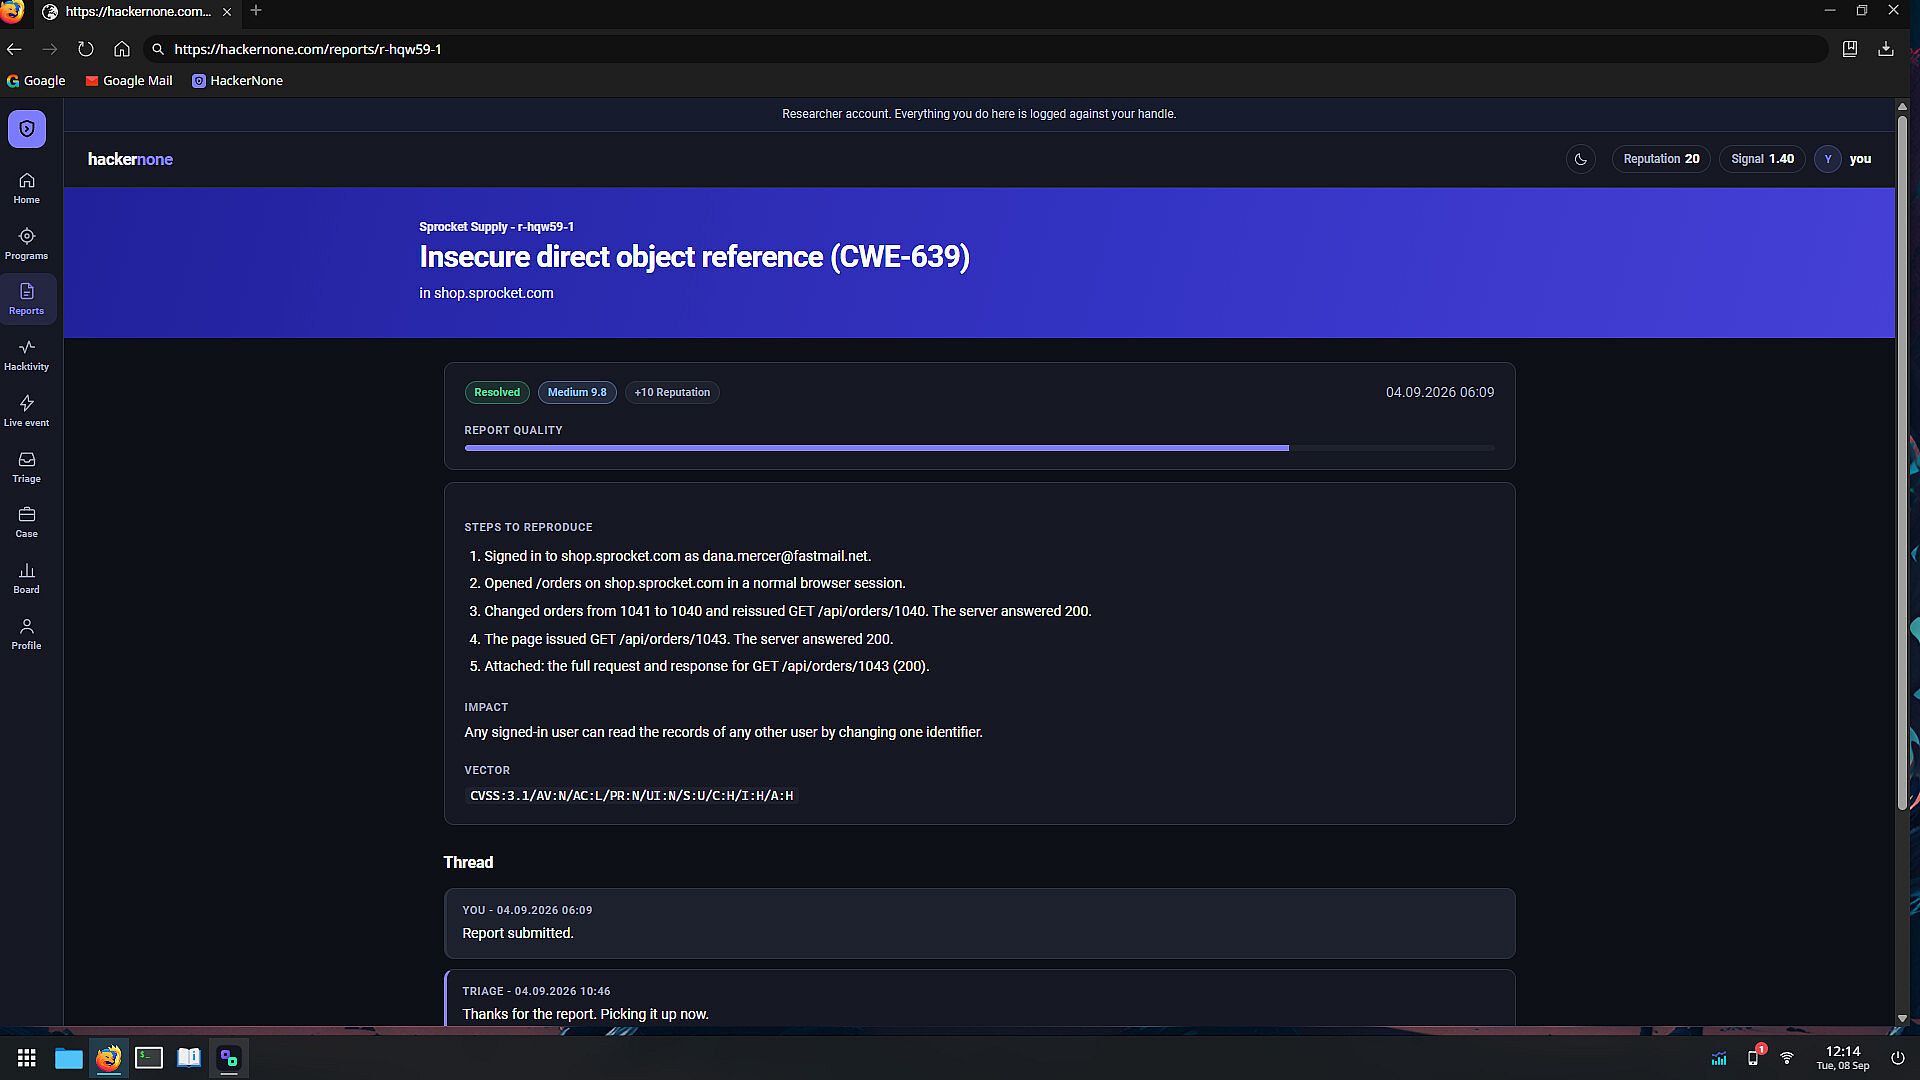
A triager reads it a few game hours later and answers in the thread. Triaged, then Resolved with a payout once they ship the fix. Needs more info, because your steps do not reproduce. Duplicate: you were right and you were slow. Informative: true, but not worth money to them. Not applicable, which is the only verdict that costs you anything.
The targets
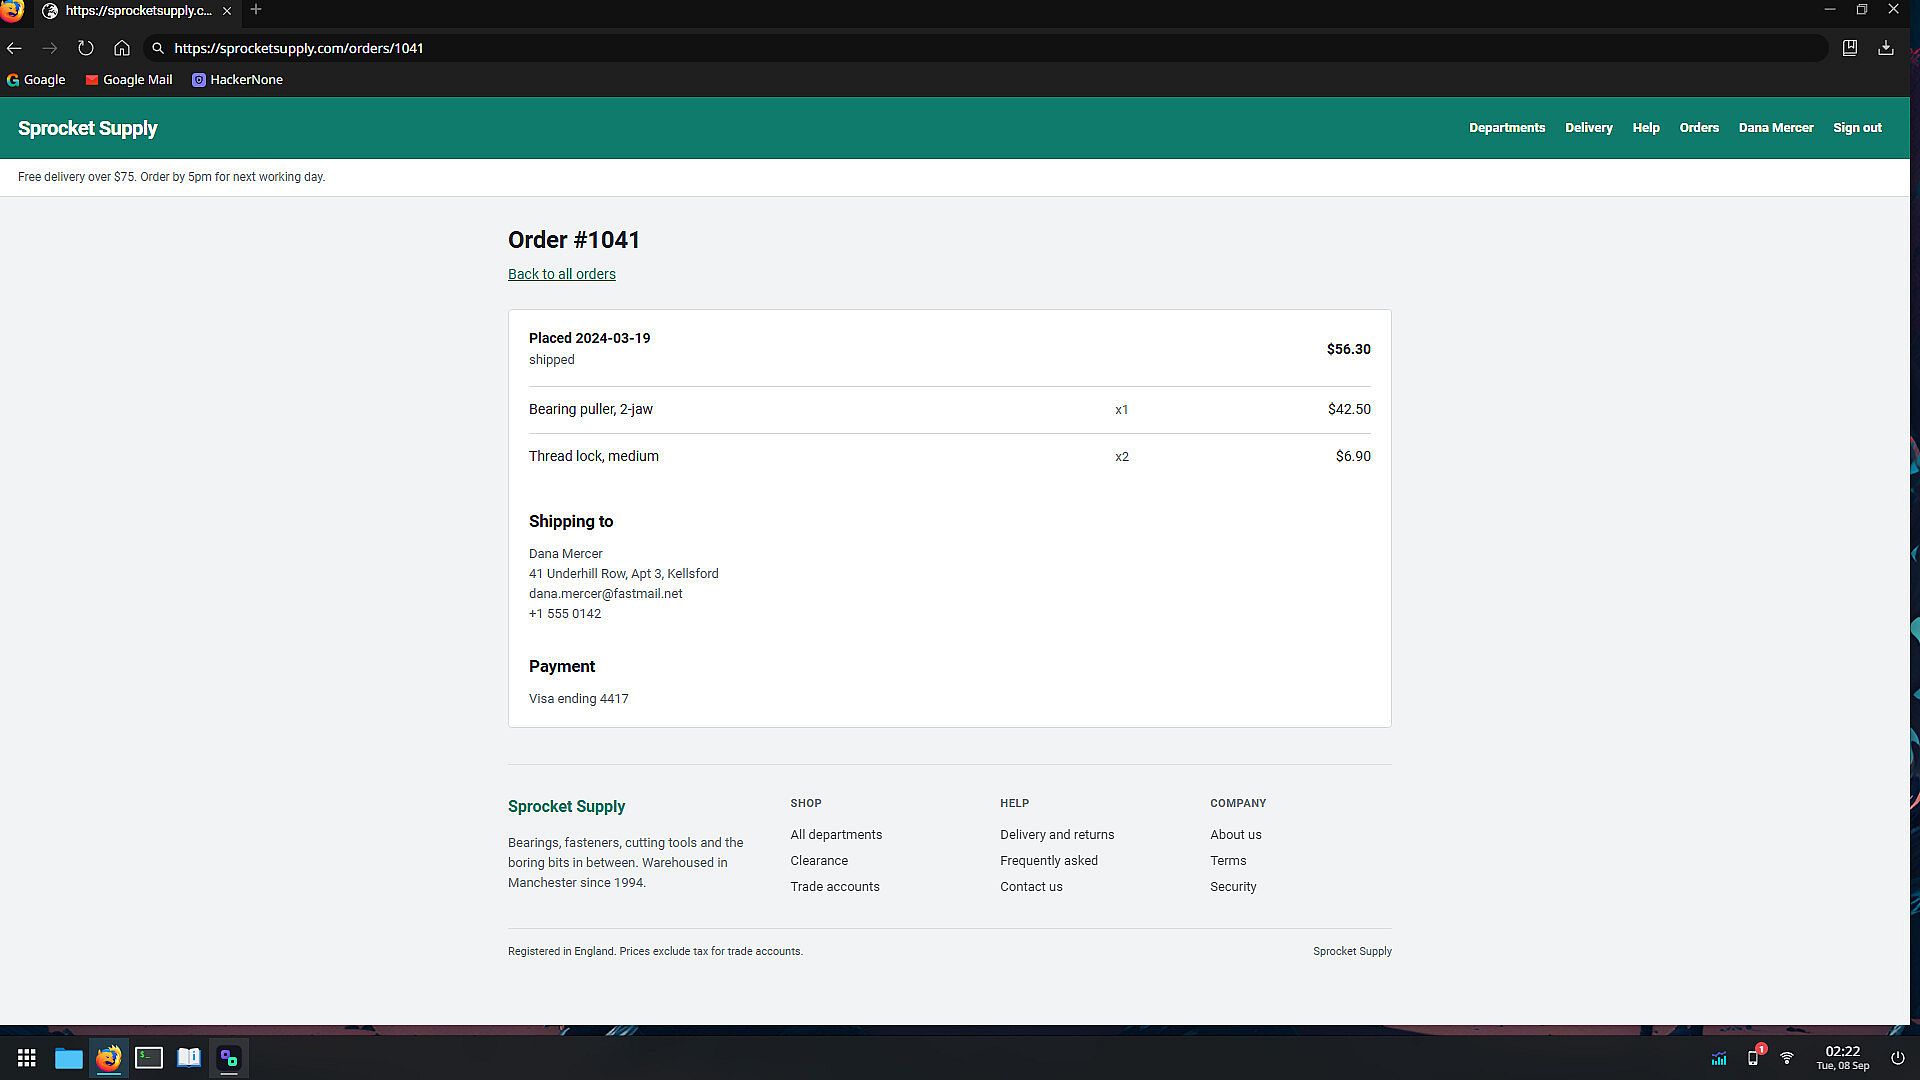
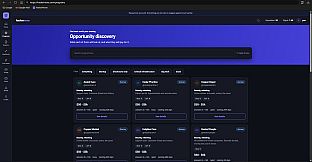
Ten companies, hand-written, roughly in difficulty order.- Sprocket Supply runs a disclosure-only programme. No bounties, forgiving triage, and an order endpoint that checks you are logged in without checking the order is yours. The tutorial lives here.
- Kestrel People and Peppermint reward recon over exploitation: admin routes sitting in a script bundle, a live mail key in shop.js, a subdomain still pointed at a host nobody owns any more.
- Lumen Notes and Atlas Docs are competent builds with one bad assumption each, in token validation and in path filtering.
- Vantage Analytics opens at 70 reputation and its bug is blind, so you will need out-of-band proof to say anything about it.
- Northwind is a marketplace with rate limits and honeypot paths that earn you a warning email if you walk into them. Anything obvious here has already been reported by someone else.
- Meridian Bank is invitation only: narrow scope, strict policy, your own account or nothing.
- Fitric has a mobile app and no web surface worth testing. Decompile the APK and work from what is in the strings.
- Corveil gives you read access to its repository. The finding is a file and a line number, and the report is a code review.
After those, procedural programmes keep arriving. Every generated company gets its own web app, API, test account and a flaw you can actually exploit, and the hunters on the leaderboard keep gaining reputation on the game clock whether you are playing or not.
Standing
Two numbers do the work. Reputation is your career total, never drops, and unlocks the tiers: startups, SaaS, big tech, critical infrastructure. Signal is the average worth of your reports, and Signal is the one with teeth. Duplicates leave it alone. Filing twenty guesses in the hope that one lands drags it down, and the programmes at the top of the ladder quietly stop reading hunters whose Signal is bad. Get it high enough and private invitations start arriving.The case
Mara Vega triages for a few of the programmes and spots a pattern in your rejections before you do. A hunter called dup3_king is filing duplicates of your reports about four minutes after you submit them, which is not possible unless somebody is reading the queue.Six chapters, ending at a case desk with two buttons and a price behind both of them. A second thread runs alongside it: Meridian closed a critical as Won't Fix, a ninety day disclosure clock starts, and someone offers you a retainer to let it run out quietly.
Everything else in the pack
- Timed live events on a single shared target, scored on severity and report quality, with bonuses for the best bug and the most creative chain, and cash and reputation for the top finishers.
- Triage work as a paid job once your Signal is good enough. Read other hunters' reports, rule on them, and get paid per correct call.
- Eight terminal tools that behave like the originals: amass, ffuf, arjun, gitleaks, jwt-tool, waybackurls, apktool, and a passive monitor that surfaces new assets days later while you are busy elsewhere.
- A sixteen article handbook on scope, severity, report writing and each bug class, plus HackTales, a writeup blog by in-game hunters that teaches the techniques without naming the targets.
- A broker who turns up after your first accepted critical, offering roughly five times the bounty for the exploit and your silence.
- Four achievements.
The companies are fictional. The bugs, the tools and the paperwork are not.